More time for effective consulting.
Pre-analysis and structuring are done faster — your time stays with the conversations that matter.
Compliance Smart Intelligence · Diagnostic
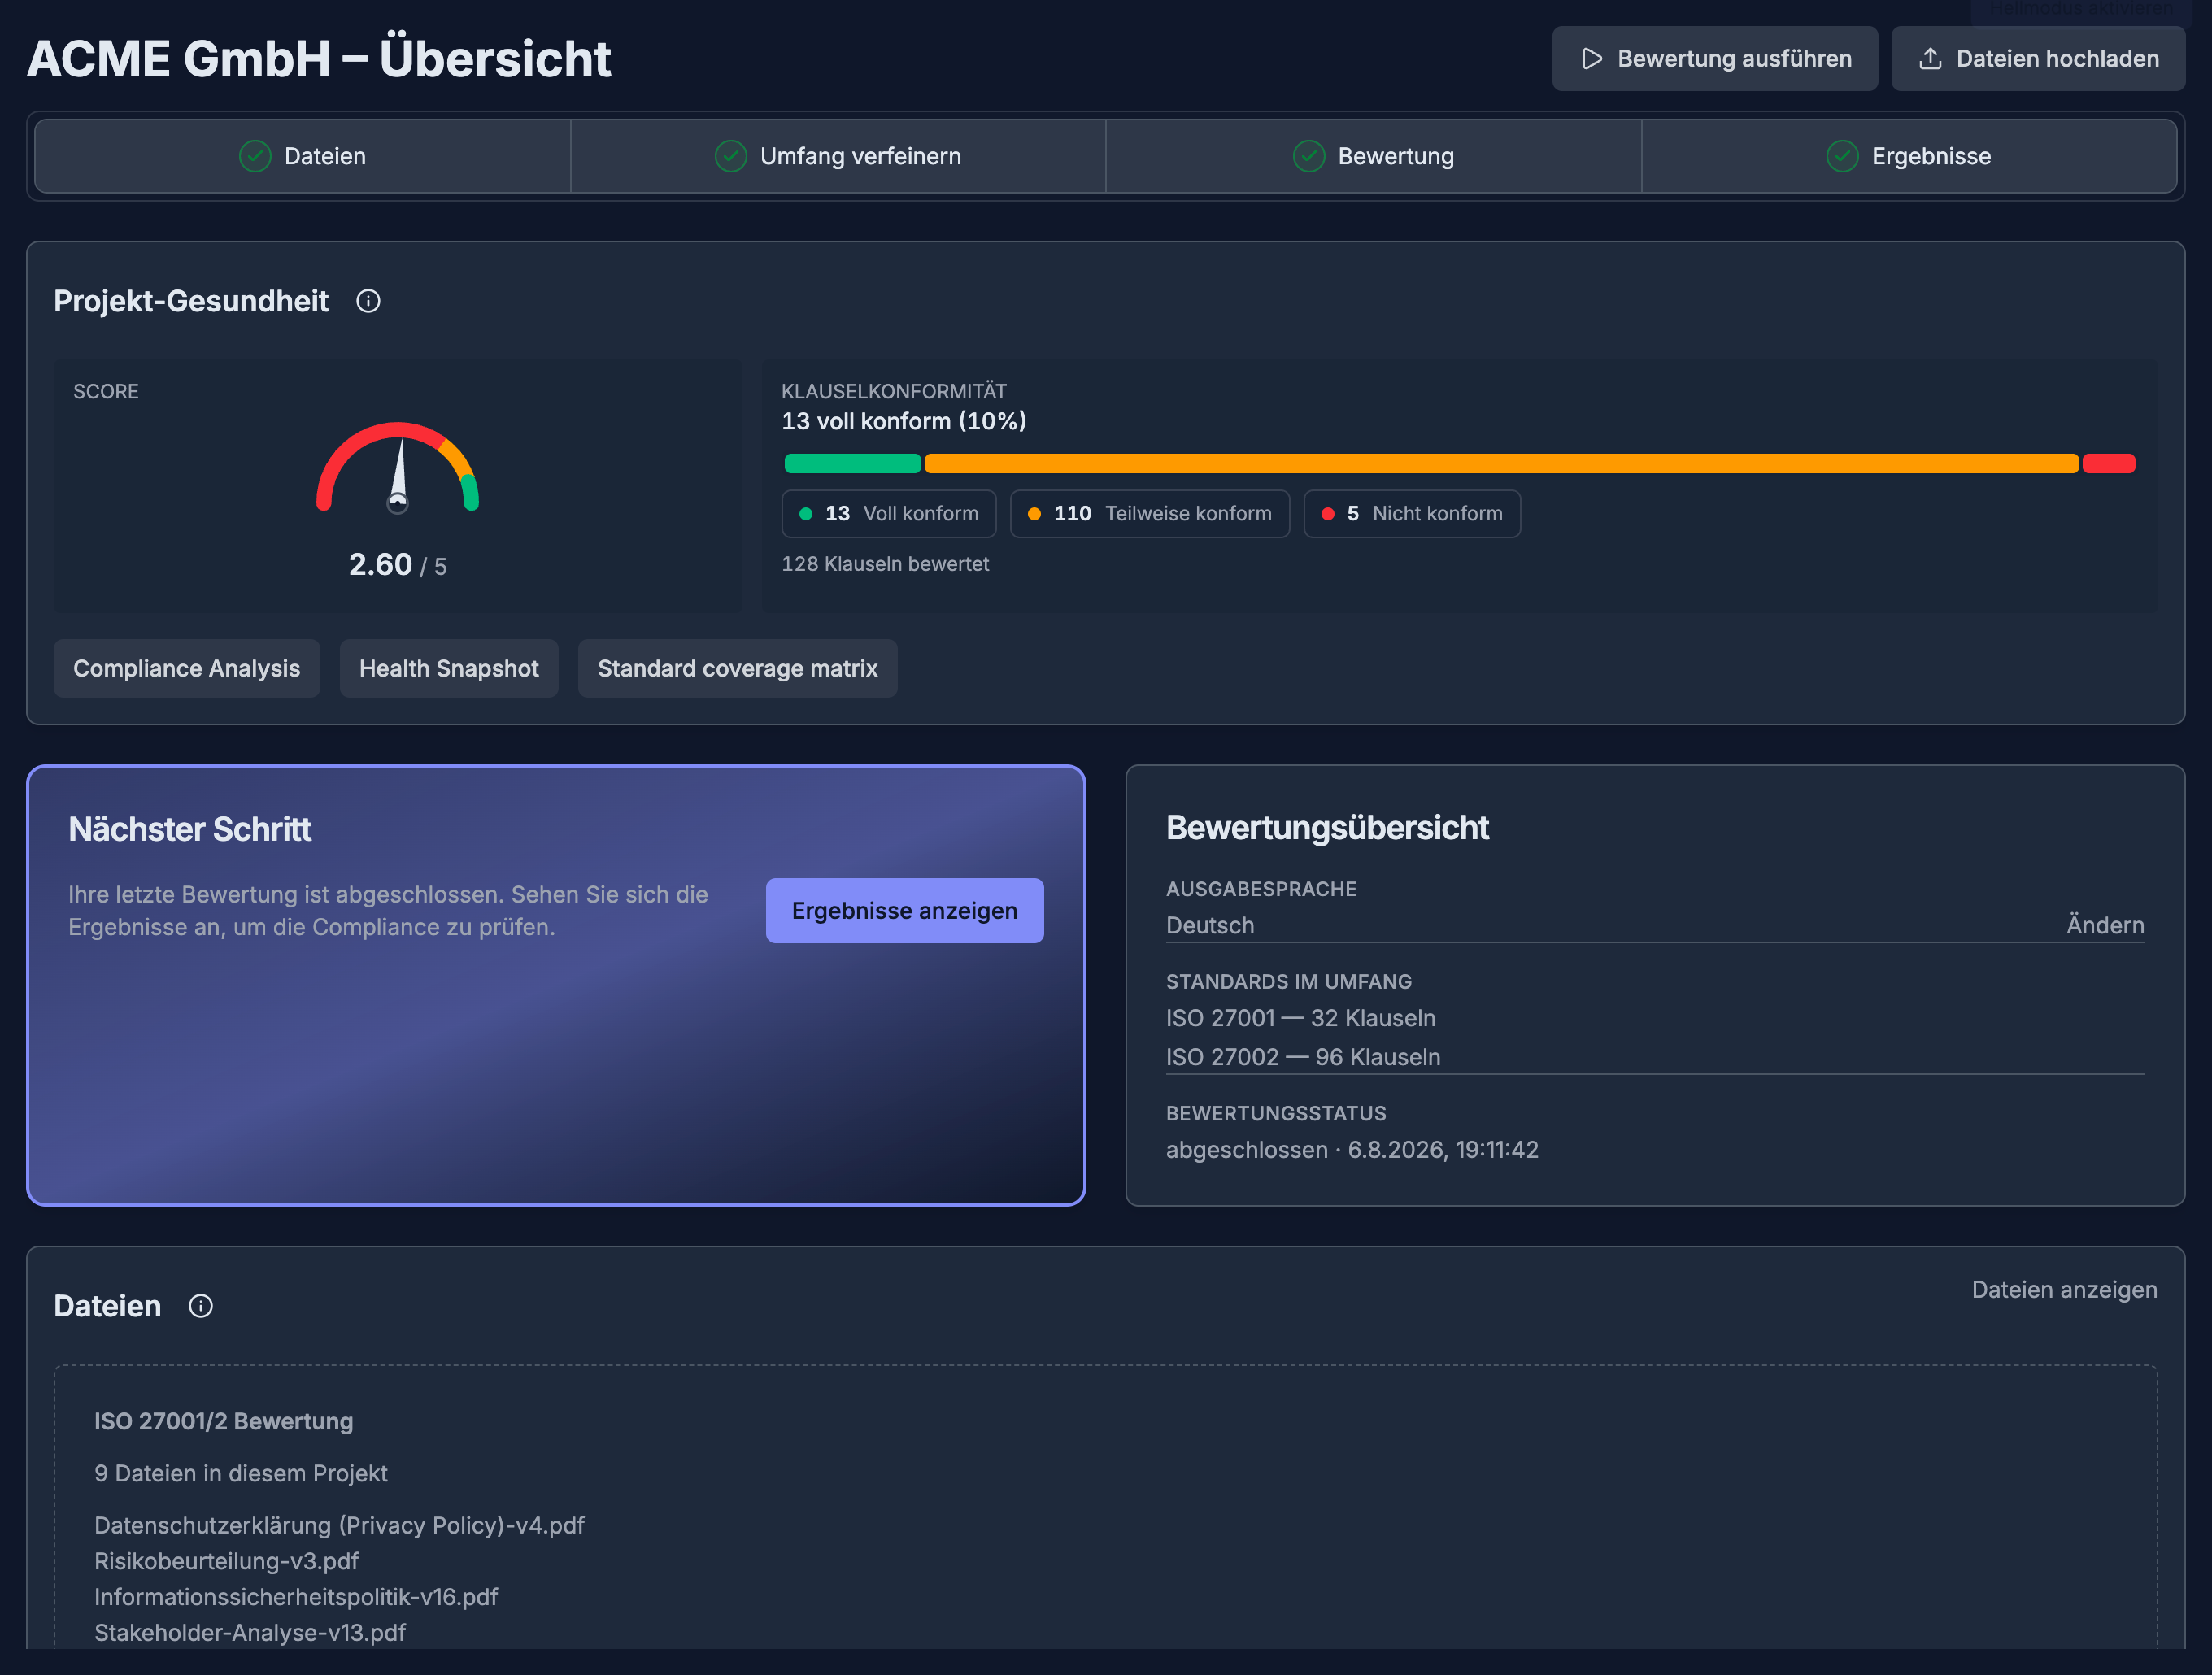
COSI DIAG reviews your existing ISMS documentation against the chosen standard — with a traceable analysis result and concrete evidence on every requirement.
For ISMS consultancies, audit teams, and information security
Standards in focus
For the requirements that drive your consulting work.Why COSI DIAG
COSI DIAG prepares existing documentation with a consistent review logic. Your expertise stays on professional judgement and advising your clients.
Pre-analysis and structuring are done faster — your time stays with the conversations that matter.
Requirement, evidence, and rating make every analysis traceable — for reliable consulting conversations.
Action areas become visible so you can assess risk and agree the next steps together.
How COSI DIAG works
From existing documents to a clear evaluation for audit preparation.
Policies, processes, and evidence form the basis of the analysis.
Your documents are checked systematically for evidence against the requirements.
You receive a score, action areas, and a clear orientation for your consulting work.
Product tour
See how a document project becomes a traceable evaluation with prioritised action areas.
No audio · 1:02 min.
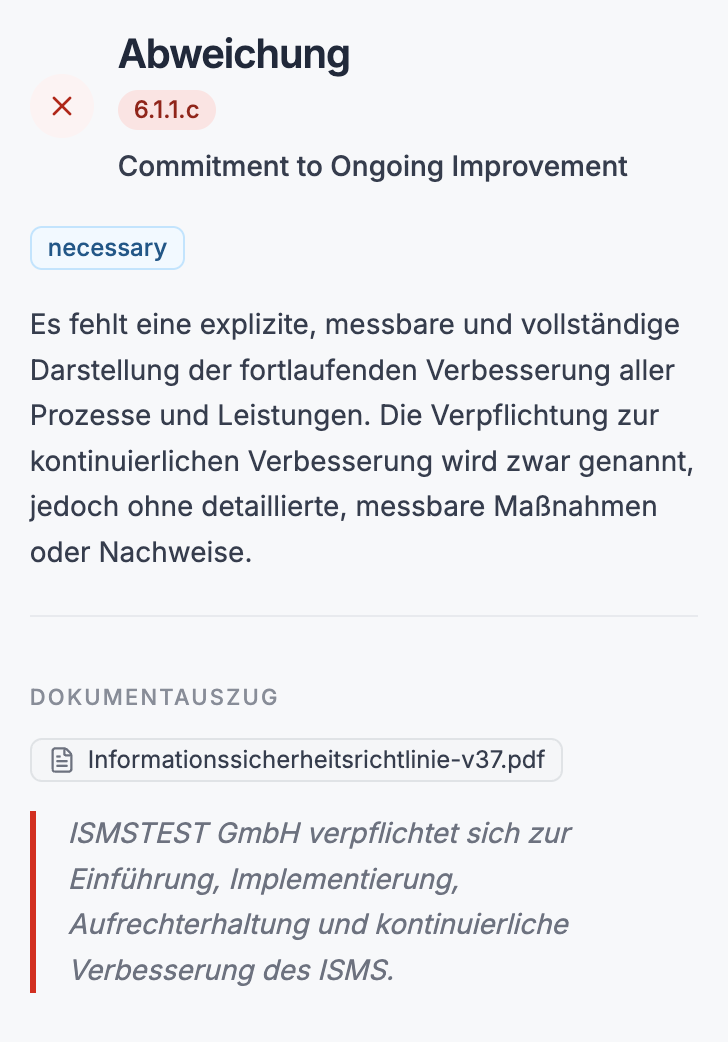
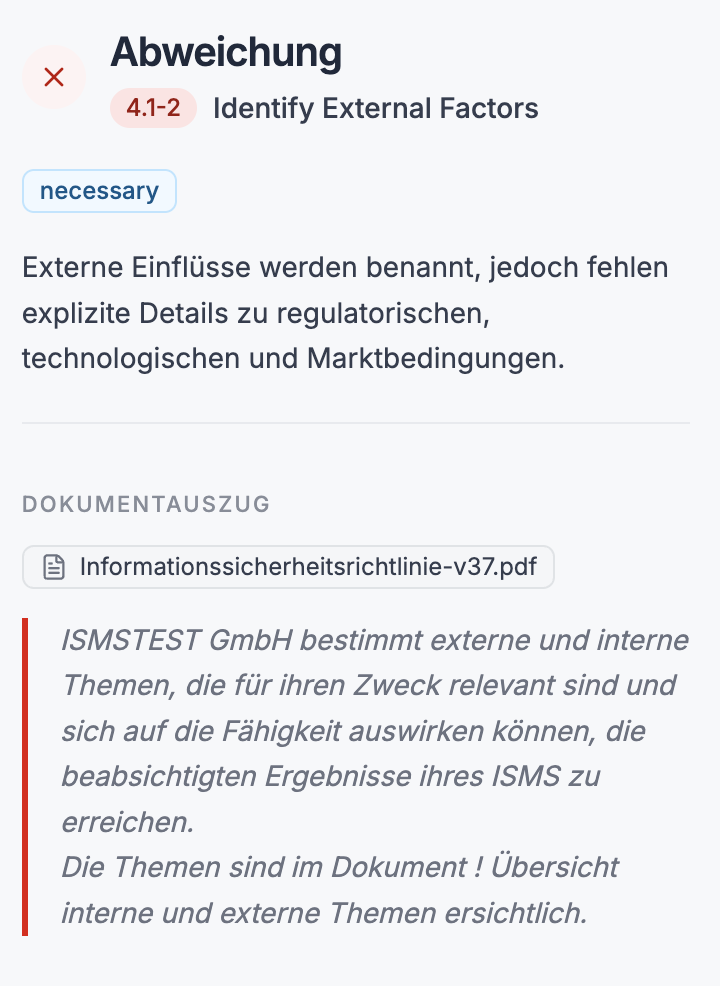
Traceable instead of gut feel
COSI DIAG does not only show deviations — it places them with a rationale and the matching document excerpt. That gives you a solid basis for the next consulting steps.
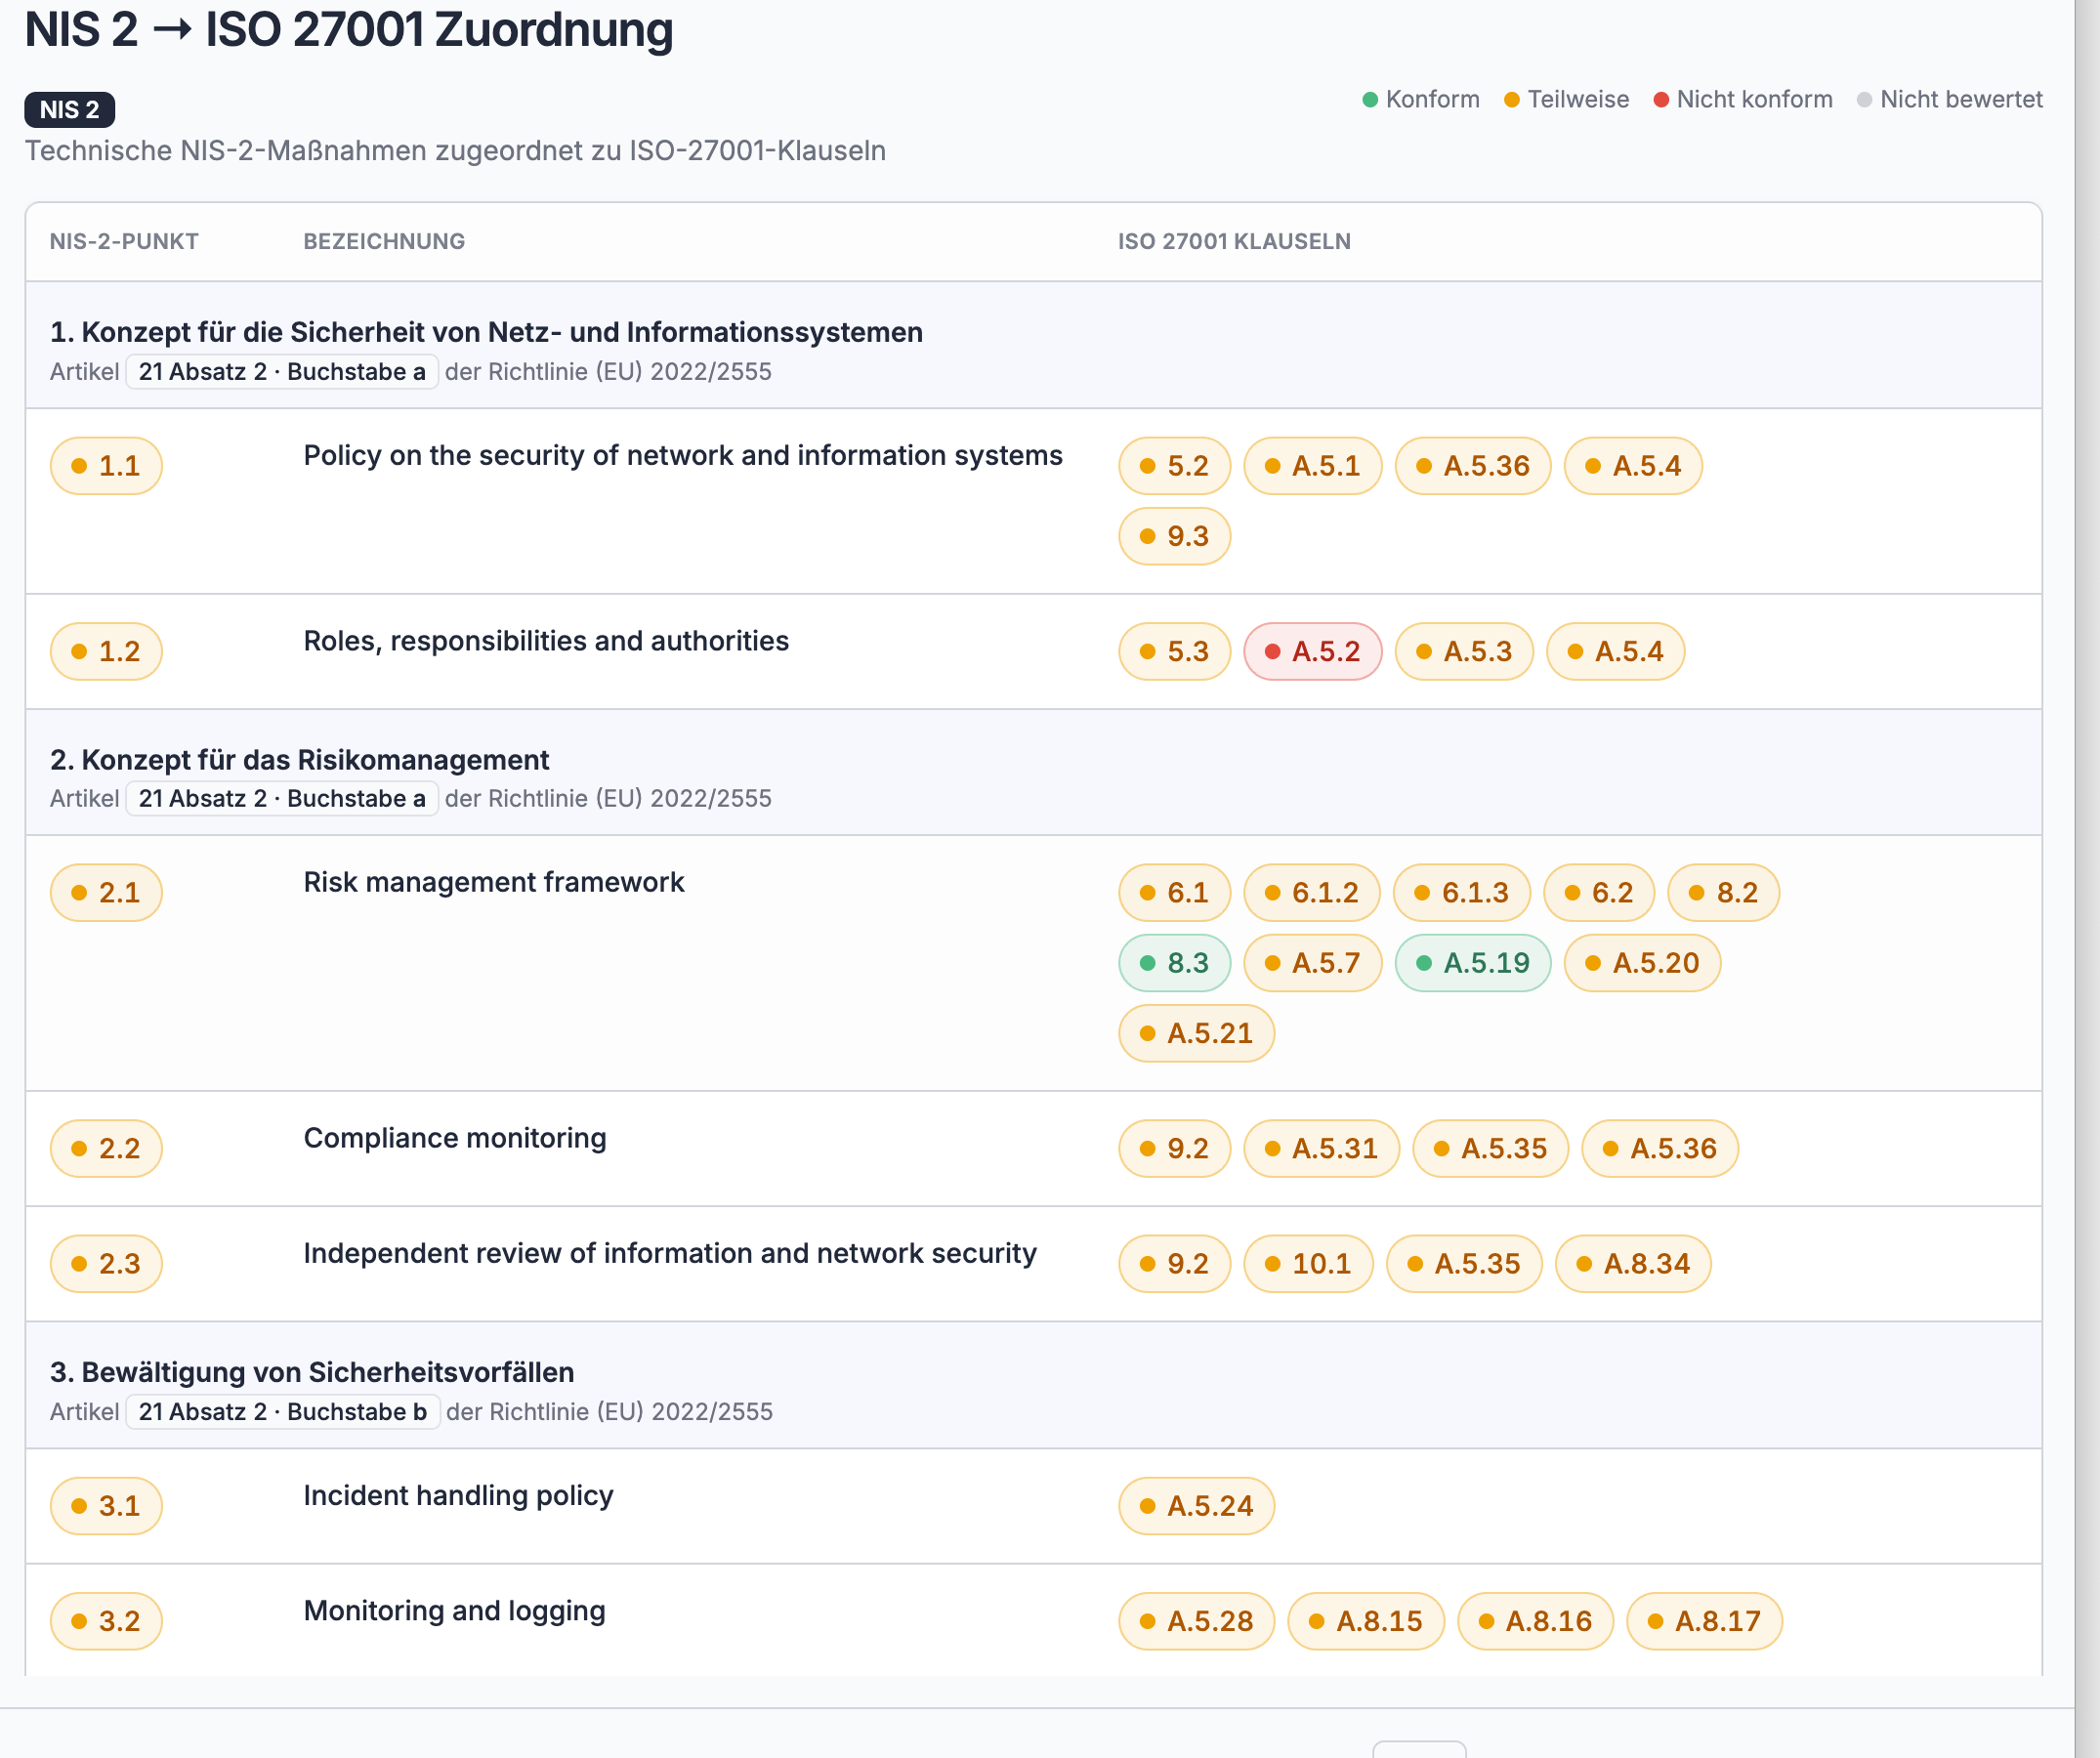
Make the connections visible
COSI DIAG shows which NIS2 requirements map to the matching ISO 27001 clauses and where extra work remains. You avoid duplicate effort and get a clear orientation for implementation.
Discuss a NIS2 use case →Data security
COSI DIAG provides a protected setting for sensitive ISMS documentation. EU hosting, separated workspaces per client, and no use of customer data for training are core principles. Details on processing and a possible on-premise option are discussed openly in a personal conversation.
COSI DIAG Platform
Whether recurring client work, ongoing review programmes, or special requirements for data sovereignty: together, we clarify how COSI DIAG expands your review capacity.
Explore the platform →Common questions
Everything you need for a first assessment — we discuss the concrete use case in person.
COSI DIAG is for ISMS consultancies, audit teams, and information-security leads who want to classify existing documentation efficiently and transparently.
A general-purpose AI chat can help with an initial review of individual documents. But when audit preparation, a complete document set, and well-founded decisions are involved, a chat alone is not enough. COSI DIAG makes results consistently traceable to requirements and evidence. This gives decision-makers a clear starting point: where action is needed, what is already evidenced, and where consulting or preparation should focus next.
You upload existing ISMS documents — for example policies, processes, and evidence. COSI DIAG reviews them systematically for evidence against the relevant requirements.
Current focus includes ISO/IEC 27001:2022, NIS2, ISO 22301, ISO 27017, and ISO 27701. Which combination fits your use case is clarified in the first conversation.
Every rating traces back to the requirement and the underlying evidence. That gives you a solid basis for professional judgement and the next consulting steps.
EU hosting, separated workspaces per client, and no training use of customer data are core principles. Requirements for data sovereignty or an on-premise option are discussed openly.
Next step
In a no-obligation first conversation we clarify your use case, relevant standards, and a suitable starting point.
Request a demo →